
Applies to: Free and Pro · Location: Users → Profile → Passkeys
Once passkeys are enabled, users manage the credentials attached to their WordPress account from the profile or account areas described below. Free covers the WordPress profile; Pro adds WooCommerce and integration account areas.
Where passkeys are managed
[ventraconnect_passkey_manage].Passkey management on the WordPress profile: the Add another passkey button, the list of registered passkeys, and Remove:
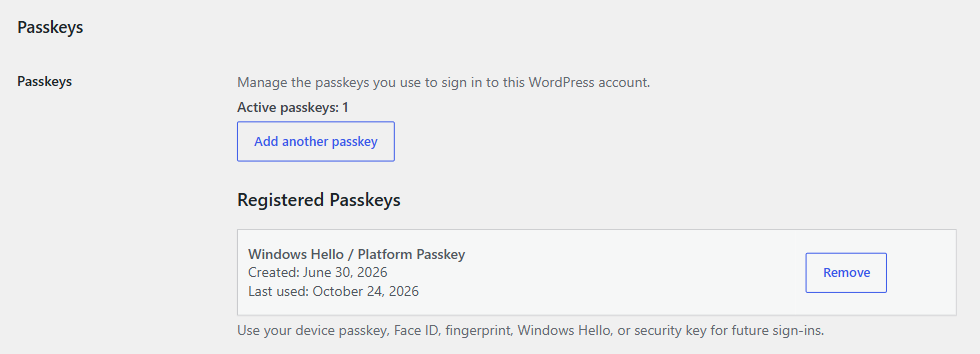
Administrators viewing another user’s profile see a read-only list. They cannot add a passkey for that user: users add passkeys from their own account.
Add another passkey
Adding more than one passkey is useful when a user signs in from multiple devices or wants a backup authenticator.
- Sign in to the WordPress account and open the profile or account area where passkeys are managed (see section 1).
- Click Add Passkey (or Add another passkey if the user already has one). The browser starts a new WebAuthn registration request.
- Choose a different device or authenticator if needed. Users can register another compatible authenticator instead of relying on only one device.
- Complete verification. After successful browser verification, the new credential is attached to the same WordPress account.
Remove a passkey
Click Remove next to the passkey. VentraConnect confirms “Passkey removed from this site. If your device still offers it, remove it from your device passkey settings too.” Users can remove only their own passkeys.
Remove credentials users no longer control, such as passkeys created on an old or replaced device.
Before removing the last passkey: make sure the account still has another working login method available, unless your site deliberately requires a different recovery process.
Using multiple devices
A passkey may be tied to a specific device, synchronised by an operating-system or password-manager ecosystem, or stored on a hardware authenticator. The exact behaviour depends on the user’s environment.
- Device-bound experience: the user may need to register a passkey separately on another computer or security key.
- Synced passkey experience: some platforms and password managers can make an existing passkey available on other signed-in devices.
- Cross-device sign-in: some browsers can offer a phone or nearby device as the authenticator for a login attempt.
Recovery and fallback
Passkeys should be part of a deliberate account-recovery strategy, especially while users are still adopting them.
- Keep Social Login, Magic Link, Email OTP, or password login available when appropriate for your site.
- Encourage users with important accounts to register more than one passkey where practical.
- Use Pro Password Phaseout carefully: do not move to stricter behaviour until users have a safe alternative to passwords.
- Before enabling Password Phaseout, verify that administrators have a working recovery method. If you ever need to restore password login for everyone, add
define( 'VENTRACONNECT_ALLOW_PASSWORD', true );towp-config.php, then remove it once the problem is fixed.
See Readiness panel & safety nets for the full Password Phaseout rollout and emergency-access guidance.
Existing users vs new users
Existing users add passkeys from their profile. This never creates a new account.
New users can create a passkey only on the WordPress registration page, and only when WordPress Anyone can register, the VentraConnect Register form placement and the Passkey Registration mode “Login & Register” all allow it. They first confirm their email (the link is valid for 30 minutes), and the account is created only after the passkey has been created.
If the email already belongs to an account, no sign-up email is sent. That user should sign in and add a passkey from their profile.
Security notes
- Removing a passkey from WordPress prevents that credential from authenticating that account through VentraConnect.
- The user’s biometric template is not stored by VentraConnect.
- The private passkey credential remains protected by the user’s authenticator.
- Users should remove credentials they no longer control, from the site and from their device.


